AI Code Reviewer
Intelligent quality gate for your GitLab pipelines
Code Review is a Bottleneck
for reviews
turnaround
through reviews
AI Code Reviewer
Automated, intelligent code review agent inside your CI/CD pipeline
Merge Request
(YAPF + Pylint)
with AST context
& quality gate
Two-Stage Quality Gate
Catch simple errors cheaply before invoking the LLM
Pylint — error detection
No LLM resources used.
Fails fast on basic issues.
AI review is skipped until this passes.
AST context + style guide
Deep semantic analysis.
Inline comments on MR.
Blocks merge if severity threshold hit.
Pipeline in Action
Three real scenarios from our test project
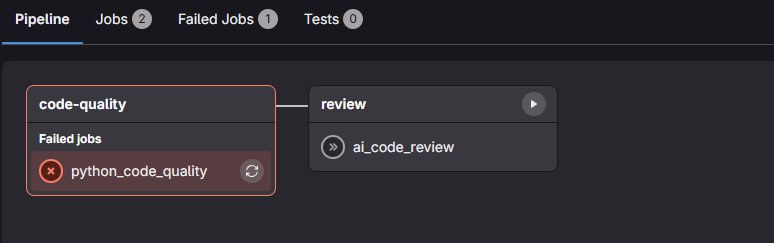
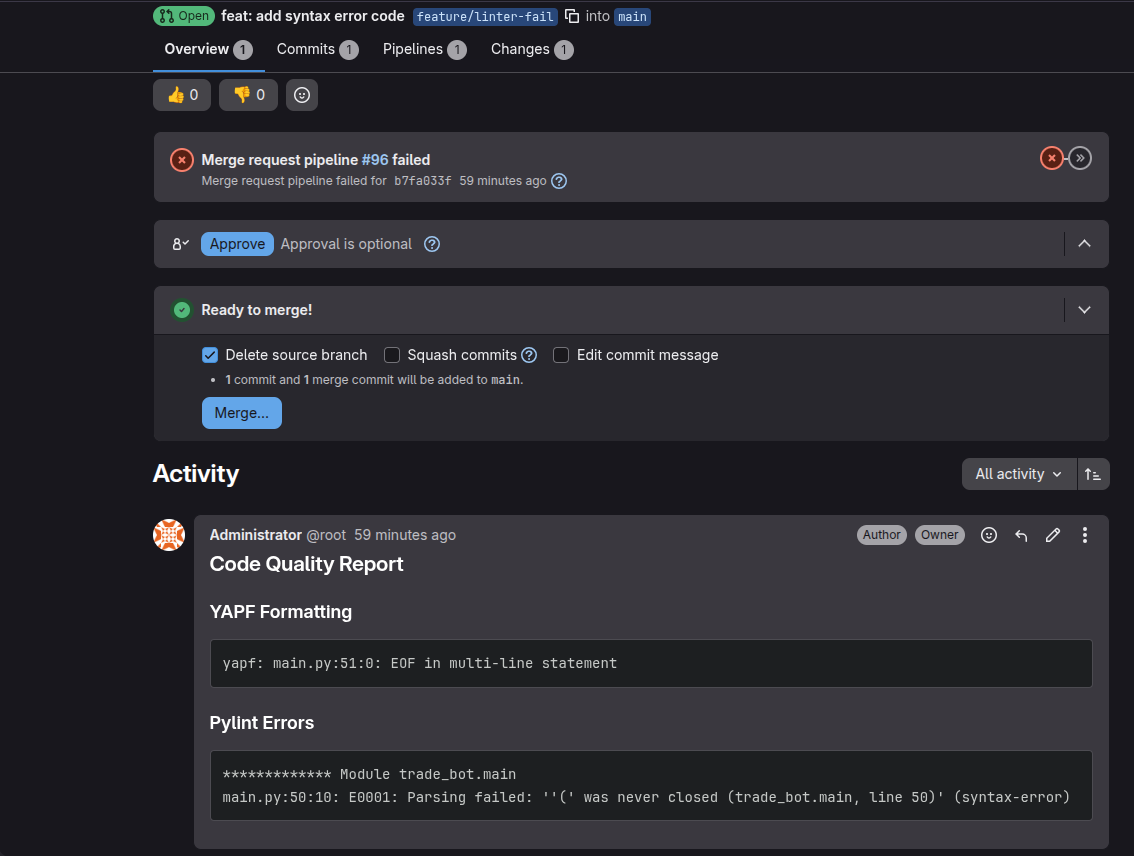
AI review skipped — zero LLM cost.
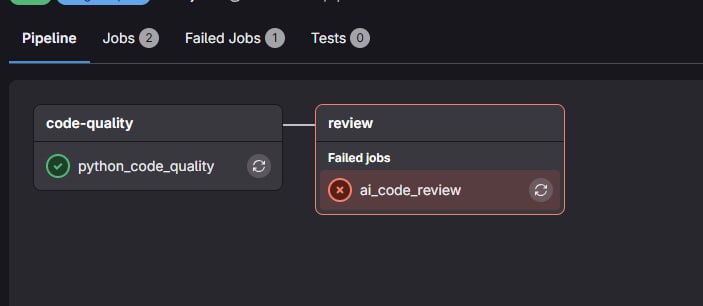
critical security issues.
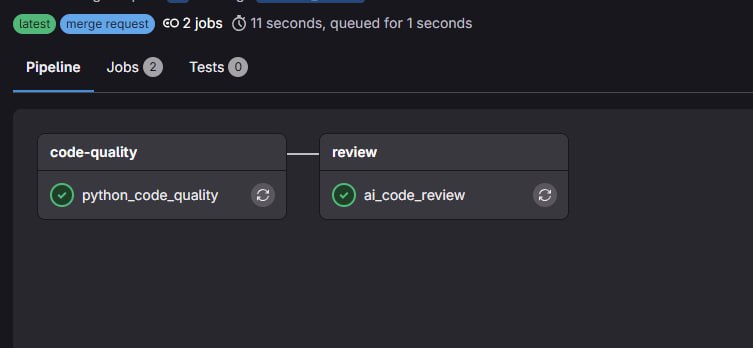
Ready to merge.
Smart Context via AST
Not just a diff — the AI sees the full picture
Without Context
LLM sees only changed lines. No idea what functions return, what types are used, or what other modules do.
High false-positive rate
With AST Context
LLM receives function signatures, class definitions, imported modules, and type info from across the codebase.
Precise, actionable findings
Multi-Provider & Auto Style Guide
Cloud AI
Anthropic Claude / OpenAI — maximum reasoning, zero infrastructure.
Self-Hosted
Ollama / vLLM — zero data leakage, code stays under your organization. Ideal for NDA / FinTech.
# Auto-generate style guide from your repo
python scripts/learn_style.py \
  --project-path /your/project \
  --output .project_style.md
# Project Style Guide (auto-generated)
## Naming
- Functions: snake_case
- Classes: PascalCase
- Constants: SCREAMING_SNAKE_CASE
## Error Handling
- Specific exception types only
- Always log, never silently catch5-Minute Setup
Add to any GitLab project — no SSH keys needed
# .gitlab-ci.yml
stages:
  - code-quality
  - review

python_code_quality:
  stage: code-quality
  image: python:3.12-bullseye
  rules:
    - if: $CI_PIPELINE_SOURCE == "merge_request_event"
  cache:
    paths:
      - .venv/
  before_script:
    - python3 -m venv .venv
    - source .venv/bin/activate
    - pip install --quiet yapf pylint
    - git fetch --depth 100 origin $CI_MERGE_REQUEST_TARGET_BRANCH_NAME:$CI_MERGE_REQUEST_TARGET_BRANCH_NAME
    - export PYTHONPATH=$(pwd):$PYTHONPATH
  script:
    - bash ci/code_quality.sh

ai_code_review:
  stage: review
  rules:
    - if: $CI_PIPELINE_SOURCE == "merge_request_event"
  variables:
    PROJECT_STYLE_PATH: "$CI_PROJECT_DIR/.project_style.md"

  script:
    - echo "🚀 Starting AI Code Review via SSH..."
    - rm -rf /tmp/reviewer
    - git clone {llm reviewer project} /tmp/reviewer
    - pip install --quiet --break-system-packages -r /tmp/reviewer/requirements.txt || pip install --quiet -r /tmp/reviewer/requirements.txt
    - cd /tmp/reviewer
    - python3 main.py
AI Agent Detects Critical Issues
SQL injection vulnerability found — inline comment with severity, impact, and fix suggestion
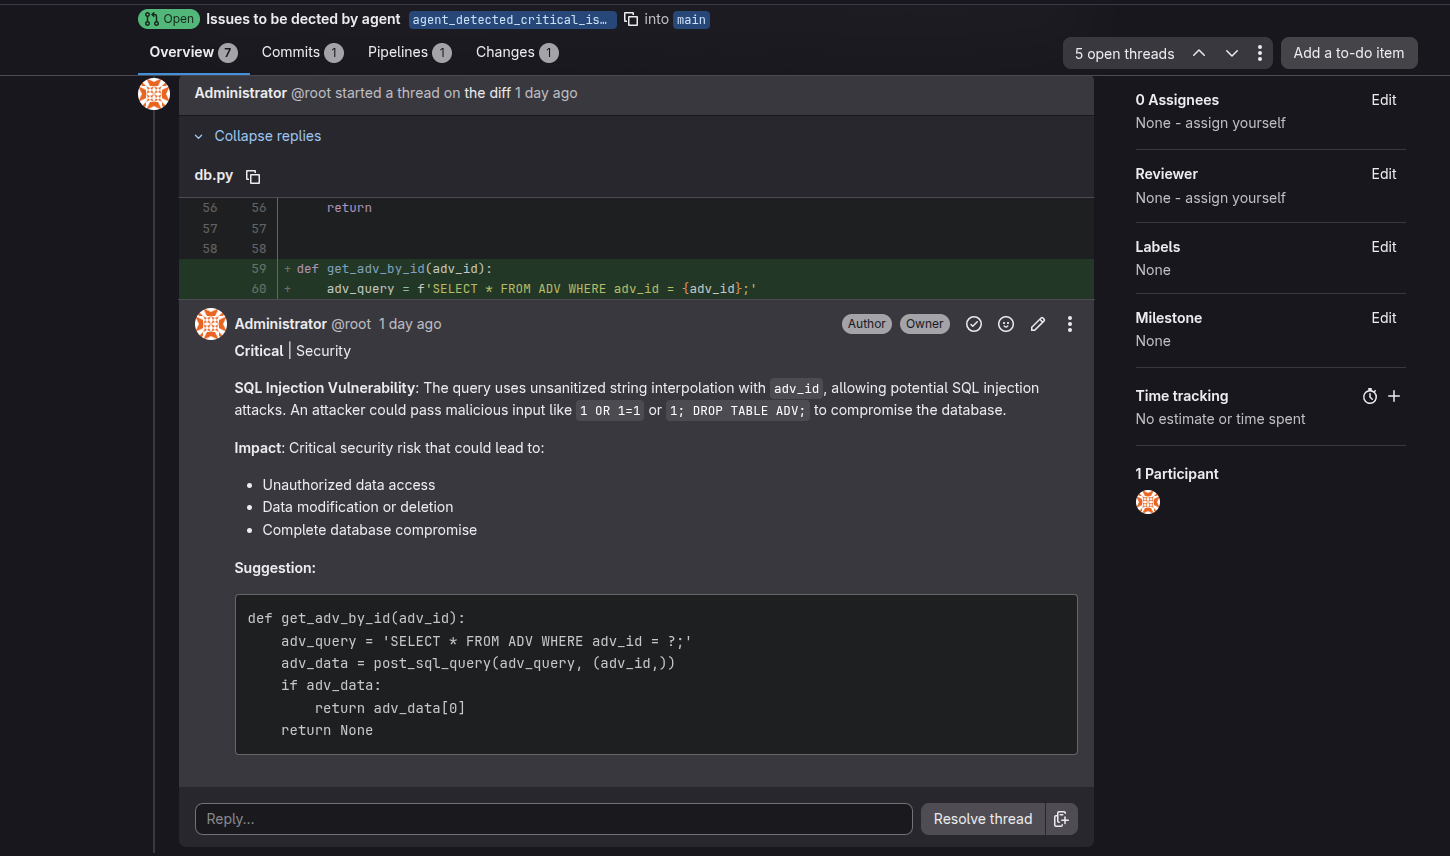
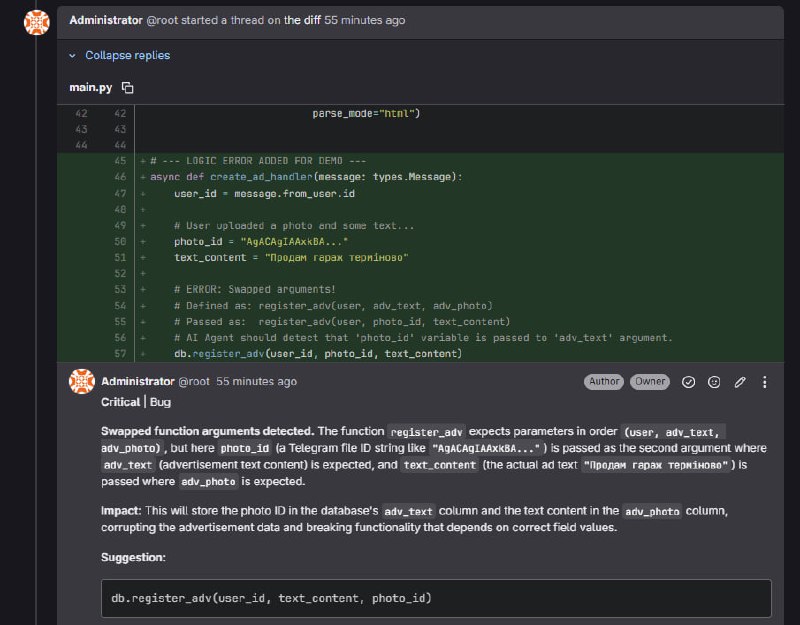
AI Agent Detects Critical AST issue
Critical type mismatch is detected by analyzing the Abstract Syntax Tree across the entire codebase, not just the diff
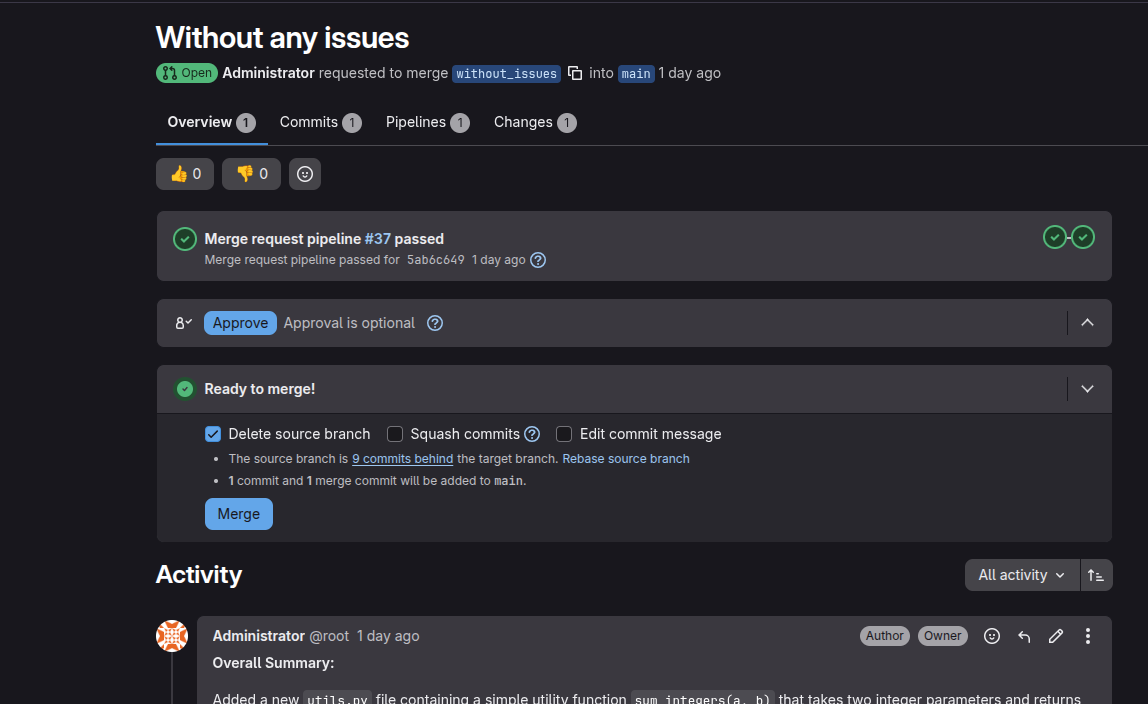
Clean Code Passes Both Stages
No issues found — summary posted, pipeline green, ready to merge
Code Quality Gate (No LLM)
YAPF and Pylint formatters catch basic issues — AI review is skipped, saving LLM resources
Impact & Scalability
Impact
Instant feedback on every MR — no waiting for human reviewers.
Consistent standards enforced 24/7 across all projects.
Security net — catches vulnerabilities before they reach production.
Cost efficient — trivial errors caught without LLM, AI only for deep analysis.
Scalability
Any GitLab project — 5-minute integration, zero infra changes.
Self-hosted LLMs — scale horizontally with your own GPU fleet.
Team-wide rollout — one reviewer repo serves all projects.